Key Takeaways
- Reliable financial AI depends on accurate, traceable, well-permissioned data.
- Human judgment is essential for decisions that can cause meaningful customer harm.
- Clear ownership makes it easier to quickly correct data, model, and reporting problems.
- Smaller organizations can begin with practical controls rather than a large governance program.
- Ongoing monitoring helps identify drift, bias, privacy issues, and security weaknesses.
Financial services organizations in the U.S. Virgin Islands operate in a close-knit business environment where customer confidence travels quickly. Whether a team supports lending, insurance, payments, customer service, fraud prevention, or back-office operations, responsible use of analytics can protect that confidence. For leaders following the work of Kirk Chewning Cane Bay Partners, the central lesson is practical: useful technology should strengthen sound decision-making, not replace accountability.
AI can help teams review information faster, prioritize cases, identify unusual patterns, and improve service consistency. Yet faster decisions are valuable only when they remain accurate, fair, secure, and understandable. A responsible approach gives organizations a repeatable way to use data while respecting customers, employees, and the unique needs of the U.S. Virgin Islands community.
Why Responsible Analytics Matters
Financial firms increasingly use AI-supported tools across credit, fraud, risk, operations, and service. In February 2026, the U.S. Department of the Treasury released a financial services AI risk management framework to encourage clearer terminology and risk-based controls. Teams can use this framework as a useful reference point when building policies that fit their size and business model.
Governance is not simply a compliance exercise. When people know where data originated, who approved a model, and how exceptions are handled, they can make better decisions under pressure. That matters especially when a customer needs a timely answer about a payment, an account restriction, or an application.
Build a Strong Data Foundation
High-quality data is accurate, sufficiently complete for its purpose, current, consistent across systems, and used with appropriate permissions. Duplicate customer profiles, missing fields, or outdated records can distort forecasts, scores, alerts, and reports.
Create a basic inventory for every important data set. It should identify:
- Its source and the method used to collect it.
- The business owner and technical steward.
- How often it changes and how freshness is checked.
- Who may access it and why.
- Which reports, workflows, or decisions depend on it?
Assign Clear Ownership
Ownership should not be vague. A data owner is accountable for business use and quality expectations. A data steward helps maintain definitions and records. An analyst interprets data, a model developer builds or maintains the system, and a business reviewer decides whether the output is appropriate for the real-world decision.
A simple responsibility chart can prevent delays. For example, a lending team may assign one employee to approve source-data changes, another to validate model results, and a manager to approve material updates before release. If a report appears wrong, everyone knows who investigates, who fixes it, and who signs off.
Make Models Easier to Explain
Customers, employees, auditors, and regulators may need a clear explanation of an automated recommendation or decision. Technical documentation is important, but plain language is equally important. A model record should state:
- Its intended purpose and users.
- The data categories it uses.
- The main factors that influence the result.
- Known limitations and situations where it should not be relied upon.
- The person or team responsible for the final review.
Explainability is also operationally useful. If staff can describe what a model does, they are more likely to notice when its output does not fit the customer’s circumstances.
Add Human Review at the Right Points
Human oversight does not mean manually checking every low-risk task. It means identifying decisions where an error could create substantial financial harm, where data is incomplete, or where the system has low confidence. Establish stop rules that pause automation and route the case to a qualified reviewer.
For instance, a fraud model may identify unusual account activity, but staff can review the available evidence before restricting an account. Employees should be trained to question automated results, document any overrides, and escalate recurring problems rather than treating the model as automatically correct.
Test for Bias and Uneven Results
Bias can enter through historical records, incomplete information, uneven sample sizes, or variables that act as proxies for protected characteristics. Before launch and throughout use, compare relevant outcomes across appropriate groups while protecting personal information.
Useful measures include approval rates, error rates, false positives, service times, manual overrides, complaints, and appeal outcomes. A large difference does not automatically prove unfair treatment, but it should trigger an investigation, documentation, and, when needed, a change to a model or process.
Protect Privacy and Limit Access
Collect only the information needed for a defined business purpose. Use role-based access, strong authentication, encryption, and regular reviews of permissions. When developing or testing a tool, use masked or synthetic data whenever real customer records are unnecessary.
Third-Party Tool Checklist
- Confirm what customer data the provider receives, stores, and uses.
- Review security commitments, access controls, and incident-notification procedures.
- Understand whether data may be used to train a vendor’s systems.
- Define audit rights, retention periods, and exit procedures before adoption.
Keep an Audit Trail and Monitor Performance
Retain model versions, data changes, testing results, approvals, incidents, customer-impact findings, and update notes in a shared system. Each record should include the dates, the responsible staff member, the reason for the change, and the approval status. This makes later reviews faster and more reliable.
Models can drift as customer behavior, fraud tactics, economic conditions, or underlying data change. Set triggers for a sudden rise in declines, fraud alerts, complaints, or manual overrides. Recent industry discussion shows financial institutions moving from isolated AI experiments to broader implementation, with governance and human oversight becoming central to responsible scaling.
A Practical 90-Day Action Plan
- Days 1 to 30: List critical data sets, AI tools, owners, users, decisions, and known risks.
- Days 31 to 60: Set documentation requirements, access reviews, testing standards, and human-review rules.
- Days 61 to 90: Run a pilot assessment, address the largest gaps, and establish a monitoring calendar.
Common Mistakes to Avoid
- Buying a new tool before defining the process it will support.
- Treating governance as a one-time project rather than an ongoing practice.
- Choosing a complex model when a simpler, more transparent method would work.
- Ignoring feedback from frontline employees and affected customers.
- Measuring speed while overlooking accuracy, fairness, privacy, and customer outcomes.
Conclusion
Responsible AI and data governance can begin with manageable steps. A current data inventory, named owners, understandable model records, proportionate human review, and regular monitoring create a solid foundation. For financial services teams in the U.S. Virgin Islands, treating trust and performance as connected goals can support the use of technology that is safer, more useful, and built to last.
- Responsible AI and Data Governance in Financial Services: A Practical Guide for the U.S. Virgin Islands
- How To Build A Strong Personal Injury Claim In Pennsylvania
- A Practical Safety Plan for Older Adults Living Alone
- 10 Examples Of Medical Malpractice That Patients Should Know
- Innovations in Advanced Urology Treatments
Key Takeaways Reliable financial AI depends on accurate, traceable, well-permissioned [...]
Key Takeaways Put safety and medical care ahead of evidence [...]
Key Takeaways Living alone can be safe when daily routines, [...]
Atlanta patients often receive care from large hospital systems, neighborhood [...]
Diagnostic Precision and Risk Stratification in Modern Urology The foundation [...]
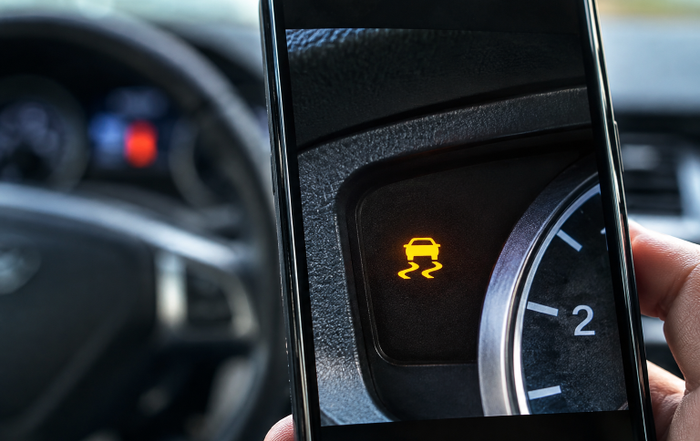
Key Takeaways A recurring SUV problem should be documented from [...]
A printed guide succeeds when it helps someone complete a [...]
Key Takeaways An arrest or citation is an allegation, not [...]